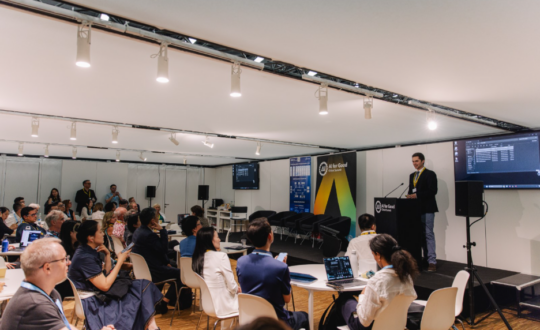
AI can strengthen cybersecurity, but it can also make attacks faster, more scalable, and harder to detect. This tension was at the heart of Trustworthy AI through AI security: The AI security nexus, a workshop organized in partnership with Cisco at the AI for Good Global Summit 2026.
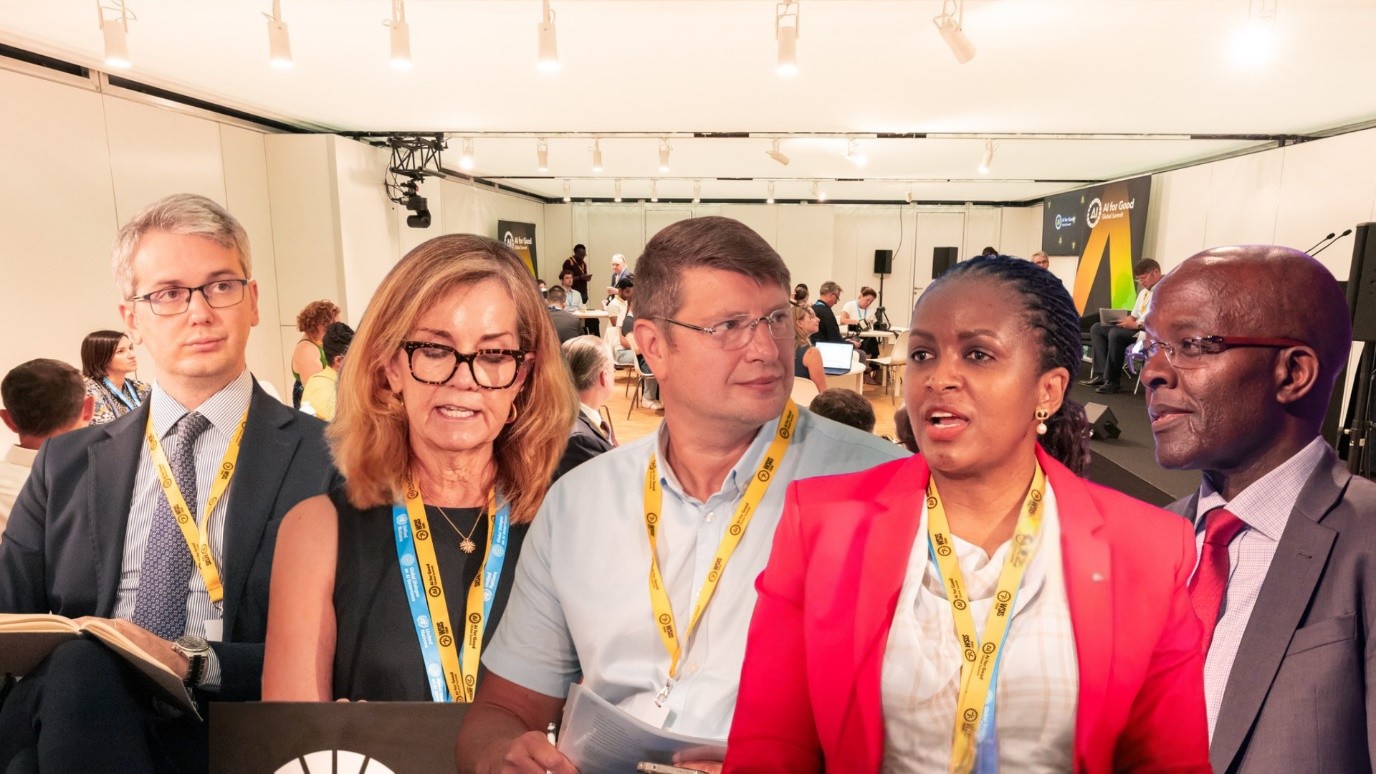
Bringing together perspectives from international organizations, government, business, standards bodies, and industry, the session examined what it takes to protect AI systems while using the technology to strengthen cybersecurity and resilience. Across their presentations and the discussion moderated by Matteo Quattrocchi, Government Affairs Director and Head of EMEA AI Policy at Cisco, the speakers emphasized that security is much harder to build into an AI system after it has been developed. It must extend across infrastructure, data, models, deployment, governance, and ongoing operations.
Security as the foundation of trust
Cosmas Luckyson Zavazava, Director of ITU’s Telecommunication Development Bureau, opened the workshop by describing trustworthy AI and AI security as “two sides of the same coin.”
“Trust is not a feature you can build on at the end of a production cycle. Trust is the foundation,” Zavazava said.
Unlike traditional software, AI systems adapt, interpret information, and make decisions. This creates attack surfaces that go beyond protecting static data. Data poisoning can manipulate what a system learns, prompt injection can bypass safeguards, and adversarial inputs can cause systems to misinterpret images, audio, or commands.
He argued that protection must be embedded at every layer. Data requires provenance and protection from tampering. Models must be robust against adversarial inputs and preserve privacy. Operational systems need continuous monitoring so that attacks or abnormal behavior can be detected after deployment.
This also requires a cultural shift away from treating speed as the primary measure of innovation. Secure-by-design development, red teaming, transparency about limitations, and global security benchmarks must become part of the development process.
Trust, he concluded, should not depend on assuming that AI is perfect. It should be grounded in systems designed to remain resilient when individual components fail or are attacked.
Building confidence through public-private cooperation
Whitney Baird, CEO of the United States Council for International Business, presented the perspective of companies operating across sectors and international markets.
She explained that AI is strengthening cybersecurity through improved threat detection, behavioral analytics, identity management, network security, and phishing detection. At the same time, it is increasing the scale and sophistication of cybercrime, creating new risks for companies, governments, and citizens.
“Trustworthy AI is not only about stopping the impact of cybercrime, but also about creating the confidence necessary for businesses, governments and individuals to embrace the opportunities that AI can offer,” Baird said.
Building this confidence, she argued, requires risk-based and proportionate governance, secure and resilient systems by design, and international cooperation that limits fragmentation. Public-private partnerships are particularly important for protecting critical infrastructure, as cyber threats cross borders and affect both national security and business operations.
When Matteo Quattrocchi asked how governments could preserve digital sovereignty while cooperating with international businesses, Baird emphasized that policymaking should involve not only AI developers, but also the companies using AI and operating critical infrastructure. She also noted that terms such as digital sovereignty can carry different meanings, making shared definitions essential to effective international cooperation.
Governments, she suggested, should establish high-level principles that protect critical infrastructure without excluding companies from global partnerships, supported by sustained dialogue as AI and its associated threats evolve.
Making AI security a development priority
Cynthia Leungo Lesufi, Minister Counsellor at the South African Permanent Mission in Geneva, focused on the priorities of Africa and the broader Global South.
AI can improve public services and support development across healthcare, education, agriculture, finance, and government. However, Lesufi argued that these benefits depend on systems that are secure, resilient, inclusive, and trusted.
From a government perspective, AI security should be treated not simply as a cybersecurity concern, but as a strategic policy issue linked to national security, economic growth, public trust, resilience, and digital sovereignty.
Her presentation called for security across the full AI stack, from infrastructure, data, and models to deployment, operations, procurement, governance, and accountability. She also stressed that African countries and other developing economies must help shape global AI standards rather than only implement decisions made elsewhere. This will require investment in skills, capacity building, technology transfer, regional cooperation, and public-private partnerships.
Asked how governments should prioritize AI security alongside other development needs, Lesufi framed the issue in terms of its broader economic and social value.
“This investment should not be seen as an additional cost. Rather, it should be seen as an investment in resilient economic growth and sustainable development of African countries,” she said.
As governments digitize essential services and critical infrastructure, insecure AI can disrupt operations, compromise sensitive data, and undermine public confidence. Building security into systems from the start is therefore more cost-effective than responding to attacks after deployment, while also creating the confidence needed to attract investment and support digital transformation.
Turning policy into technical standards
Igor Minaev, Director of External Relations at ETSI, examined how international standards can translate broad policy goals into technical requirements.
Minaev presented ETSI’s framework for AI cybersecurity, which addresses AI-specific threats across the system lifecycle, from design and development through deployment, maintenance, and end of life. It also defines responsibilities for developers, system operators, data custodians, users, and other participants in the AI supply chain.
The development of such standards depends on cooperation among governments, industry, academia, cybersecurity agencies, and international standards organizations. AI is a global technology, Minaev argued, and its security cannot be addressed effectively through isolated national approaches.
He also described a shift from traditional, one-time conformity assessments toward continuous assurance. AI systems change during operation, and emerging regulations increasingly require products to remain compliant throughout their lifecycle rather than only when they enter the market.
When Quattrocchi asked how standards developed by different organizations could become complementary rather than duplicative, Minaev emphasized the need for sustained coordination. Safety, cybersecurity, software engineering, and AI expertise must be brought into a coherent system capable of supporting continuous assurance.
“Trustworthiness is not created by regulation alone. It is not created by technology alone,” he said. “It is created when policy, engineering, cybersecurity, and international standards evolve together.”
Responding to a faster threat landscape
Matteo Quattrocchi, Government Affairs Director and Head of EMEA AI Policy at Cisco, concluded the presentations with Cisco’s perspective on the rapidly changing AI security environment.
He described AI security as a whole-of-infrastructure challenge that begins with data centers and extends through datasets, models, networks, applications, and autonomous agents.
Existing threats such as phishing are becoming more sophisticated through generative AI, while emerging systems are creating new vulnerabilities. Data poisoning and prompt injection can compromise AI during development or use. Agentic AI expands the attack surface by allowing systems to act with greater autonomy, while open protocols connecting AI tools with external systems can introduce additional points of exposure.
Quattrocchi placed particular emphasis on the shrinking window between the discovery of a vulnerability and its exploitation. Processes that once took months or years may now happen within hours, increasing the need for continuous monitoring and rapid response. The momentous change brought by highly capable AI models in cybersecurity is only accelerating this trend.
Older hardware and software can also create systemic vulnerabilities, particularly in critical infrastructure. Governments and companies therefore need to address technical debt while modernizing the systems supporting communications, energy, transport, water, and other essential services.
“Secure AI is built on a secure and resilient infrastructure, these are foundational aspects of AI trust, adoption and success” Quattrocchi said.
Across the workshop, the speakers returned to the same conclusion: trustworthy AI cannot be achieved through technology, regulation, or standards in isolation. Security must be built into the full AI lifecycle and supported by continuous monitoring, clear accountability, international cooperation, and investment in skills and infrastructure.
The challenge is not only to protect AI systems from attack, but also to create the confidence needed for governments, businesses, and communities to use them responsibly. Turning that ambition into practice will require coordinated action across the public and private sectors, with countries at every stage of digital development involved in shaping the systems and standards that will govern AI.